When cybersecurity comes up in a board meeting, “How secure are we?” seems like a reasonable question. But what does the answer actually tell directors? A simple assurance that security measures are in place does not explain which risks could harm the business, whether those risks are being managed, or what decisions the board needs to make.
Cybersecurity governance for boards means more than receiving a general security update. Directors need to ask questions that help them challenge assumptions, understand the evidence, and hold management accountable for the risks the organization faces.
Cybersecurity governance for boards means more than receiving a general security update.
The World Economic Forum’s Global Cybersecurity Outlook 2026 found that ‘23% of public-sector organizations reported having insufficient cyber resilience capabilities.’ This makes it important for boards to look beyond reassurance and examine what their organization can actually demonstrate.
Here are six questions that can make those conversations more useful.
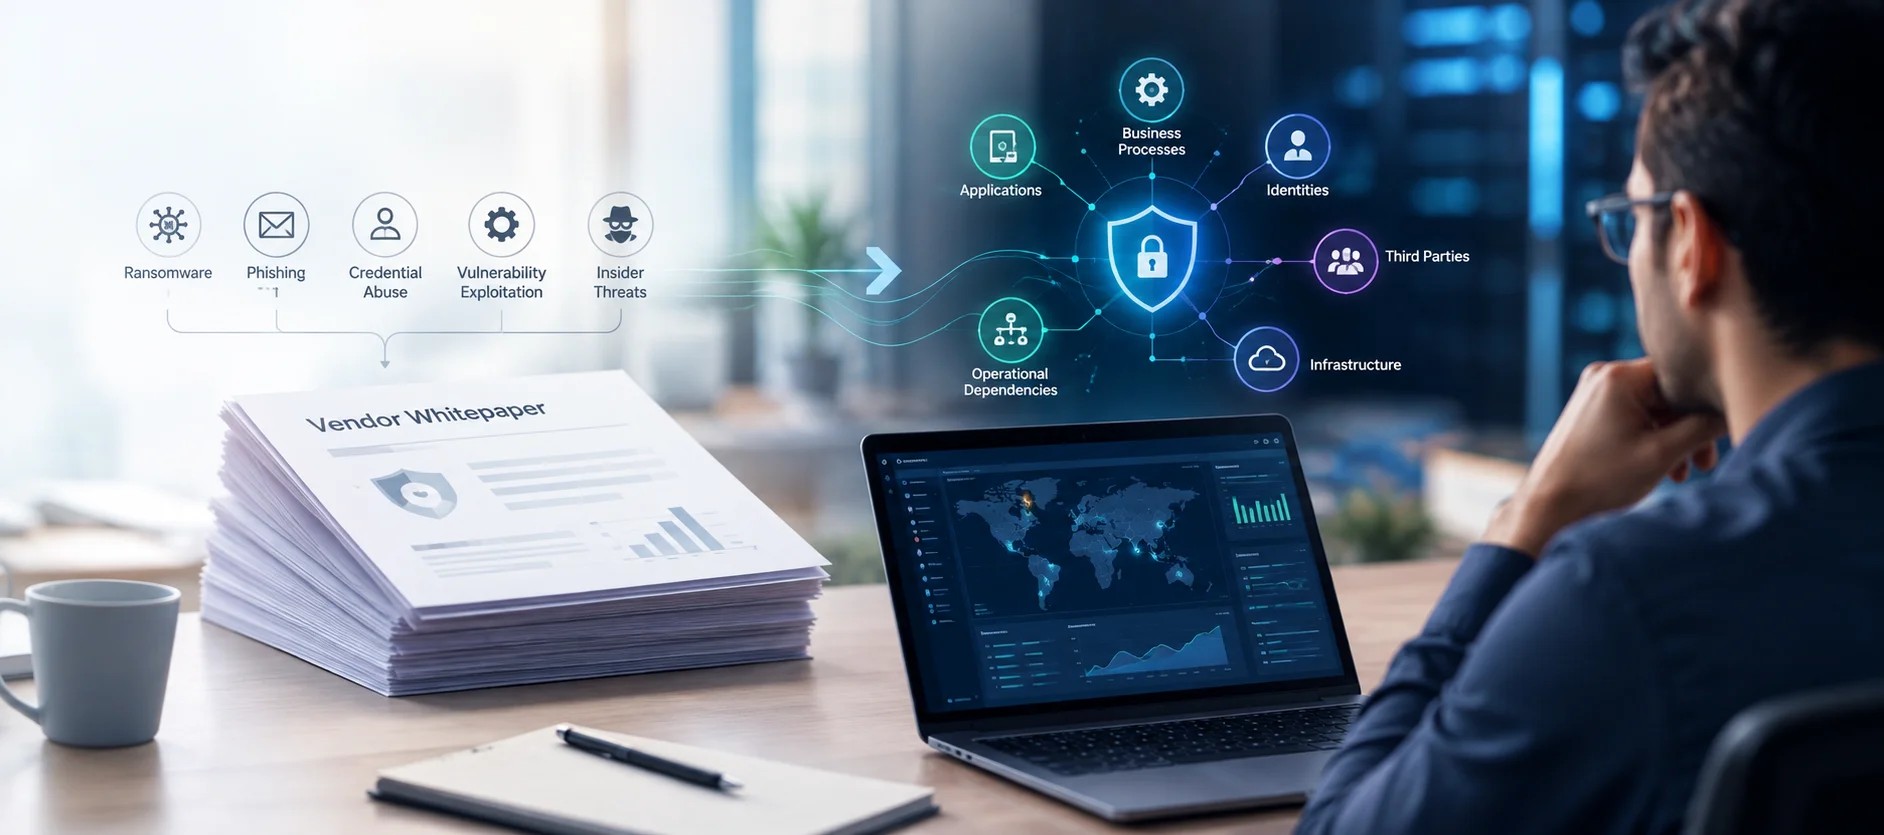
A general list of cyber threats does not tell the board which ones matter most for the business. The impact of an incident depends on what the organization does and which systems, information, and processes it relies on. Cybersecurity governance for boards starts with that specific picture.
For a manufacturer, an interruption to production systems could halt operations. For a financial services organization, compromised customer information or disrupted transactions could cause serious harm. The board needs to understand these business consequences, not just the technical threats behind them.
Ask management:
The answers should help directors understand the organization’s most significant exposures and whether management is prioritizing them appropriately.
Once the board understands the risks, it needs to know whether the organization’s spending addresses them. A large cybersecurity budget, new tools, or completed assessments do not automatically mean the business is better protected.
Management should be able to explain what each major investment is intended to achieve, which risk it addresses, and how its effectiveness will be assessed. Directors should also understand what remains unresolved when funding or resources are limited.
Ask management:
This moves the discussion from how much the organization spends to whether that spending supports its business priorities.
Management may report that security controls are in place, assessments have been completed, and employees have received training. These activities matter, but they do not prove that the organization’s most important risks are under control.
The board needs evidence of what those activities have revealed and what happened next. If an assessment identifies serious weaknesses, for example, directors should know whether they have been fixed, who is responsible, and when unresolved issues will be addressed. Independent reviews and structured crisis exercises often expose weaknesses that routine reporting misses.
Ask management:
The aim is not for directors to interpret technical reports themselves. It is to establish whether management’s assurances are supported by evidence and whether identified weaknesses are receiving appropriate attention.
No security program can guarantee that every incident will be prevented. Boards therefore need to understand not only how the organization protects itself, but also how it will respond when something goes wrong.
A good response plan sets out who has the authority to act, which operations must be restored first, and how decisions involving customers, regulators, and business continuity will be handled. The board should also know whether these arrangements have been tested.
The UK government’s Cyber Security Breaches Survey 2025/2026 found that “Formal incident response plans were less widespread (25% of businesses; 19% of charities).” Although the figures are UK-specific, the point applies more widely: boards should check that response plans exist and have been tested, rather than assuming that the organization is ready.
Ask management:
The important question is whether the organization can act effectively under pressure, not simply whether a response plan exists.
An organization can manage its own systems carefully and still face disruption because it relies on suppliers, service providers, or business partners. If one of those providers suffers an incident, the organization can lose an essential service even when its own systems remain secure. WEF’s Global Cybersecurity Outlook 2026 in its survey found, that “65% of large companies by revenue indicate third-party and supply chain vulnerabilities are their greatest challenge, which has risen from 54% in 2025.”
Boards should understand these dependencies and whether management has assessed the consequences of a supplier becoming unavailable or unable to protect the information it handles.
Ask management:
This helps directors understand where the organization relies on others and whether those dependencies could undermine its ability to operate.
Even a well-understood risk can remain unresolved if nobody is clearly responsible for managing it. This is especially common in cybersecurity, where decisions often cross security, technology, finance, legal, and operational teams. When responsibilities are unclear across those teams, actions get delayed and important decisions sit unresolved.
That is where the board’s role begins. The board does not need to manage every security issue itself, but it does need to know who owns significant risks, which decisions require board approval, and when an unresolved issue must be escalated.
Ask management:
Clear ownership gives the board a way to track whether decisions lead to action, and to distinguish between risks that have been consciously accepted and those that remain unaddressed. Without that clarity, the first time the board hears about a serious incident may be from a journalist.
To understand the impact of these questions better, consider an organization whose supplier suffers a cyber incident. The organization’s own systems remain secure, but it loses access to a service needed for a critical business process.
Management reports that the incident is being handled. Rather than accepting that at face value, the board asks two questions: how long the business can continue without the service, and whether a workable alternative has been tested. The answers show that no alternative has been tested, and that nobody inside the organization has clear authority to approve a workaround.
With these gaps in view, the board can act. It can require management to assign a specific owner for the contingency, build and test a workable alternative, and report on progress at the next cycle. A broad question about security would not have surfaced any of this. The specific questions did.
The purpose is not to give directors more technical detail. It is to help them understand exposure, challenge assurances, and ensure that significant risks lead to action.
The purpose is not to give directors more technical detail. It is to help them understand exposure, challenge assurances, and ensure that significant risks lead to action.
Supporting that work is where our advisory practice focuses. At Silverse, our Cyber Strategy and Consulting services include Board & C-Suite Advisory & Reporting, giving directors informed oversight through risk metrics, performance indicators, and regular reporting.
Get in touch with us to discuss your organization’s cybersecurity governance and reporting needs.
Why is “How secure are we?” not enough for boards?
The question invites a broad assurance but does not reveal which risks could harm the business, whether security measures are effective, or what decisions are needed. Boards need specific answers supported by evidence.
Which cyber risks should the board focus on first?
Boards should focus on risks that could cause significant financial or operational damage. They should understand which critical systems and processes are exposed and how management is prioritizing those risks.
How can boards assess whether cybersecurity spending is effective?
They should ask which risks an investment addresses, what improvement it is expected to deliver, and what evidence will show whether it has made a difference.
What should boards ask about cyber incident response?
They should establish who can make critical decisions, which operations must be restored first, and whether response and recovery plans have been tested.
Why is accountability important in cyber risk oversight?
Clear accountability ensures that significant risks have owners, unresolved issues are escalated appropriately, and decisions lead to action rather than remaining open.
Please fill the details below. A representative will contact you shortly after receiving your request.