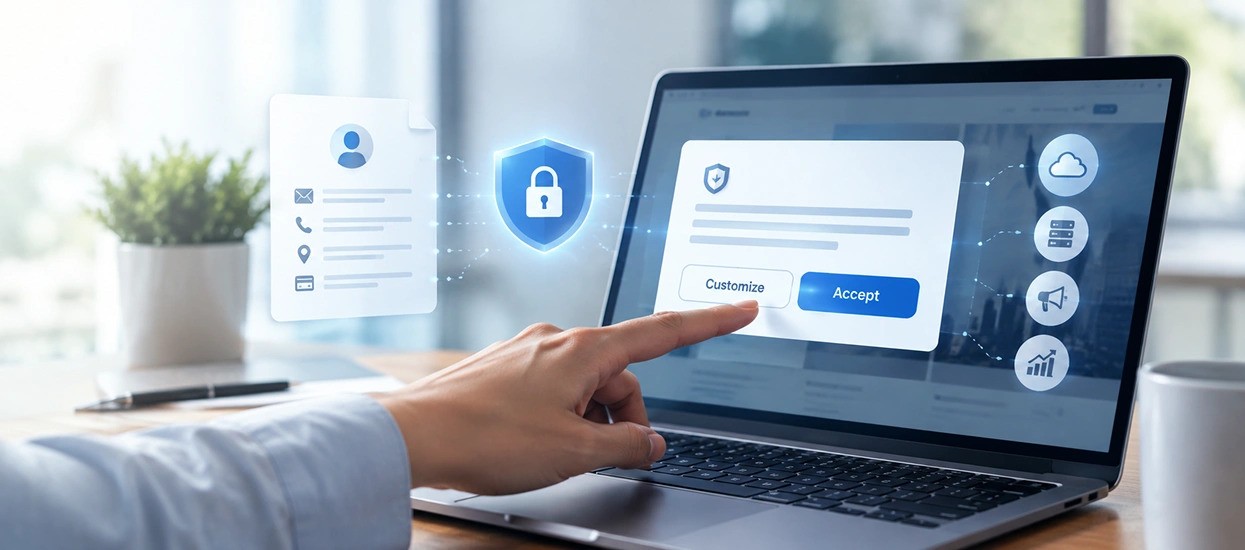
A DPDPA consent banner can create an illusion of readiness. The website asks for permission under India’s Digital Personal Data Protection Act, 2023 (DPDPA). The user clicks “Accept” and somewhere a consent event gets recorded. From the outside, the organization appears to have dealt with consent.
A banner can collect a response. Compliance depends on whether the organization can govern what follows.
But the difficult questions start after the click.
What exactly did the person agree to? Can that decision be connected to a specific purpose? Where does the personal data travel next? What happens if consent is withdrawn six months later?
A banner can collect a response. Compliance depends on whether the organization can govern what follows.
A single “I agree” button cannot resolve unclear processing behind it.
The problem begins when organizations treat consent as an interface requirement.
Section 6(1) of the Digital Personal Data Protection Act, 2023 describes consent as “free, specific, informed, unconditional and unambiguous with a clear affirmative action.”
That standard changes the question.
Consider a customer giving a mobile number to receive an order update. Using that number for the requested update is one context. Adding the same number to an unrelated marketing workflow is another.
A single “I agree” button cannot resolve unclear processing behind it.
Many consent journeys fail before data even enters the organization.
A DPDPA consent banner may be clearly visible, yet the accompanying language may say little more than “We value your privacy” or “We use your information to improve your experience.”
Those statements sound reassuring but do not explain much.
Rule 3 of the Digital Personal Data Protection Rules, 2025 requires “an itemized description of such personal data” and identifies the “specified purpose or purposes” as part of the notice requirements.
A team should, therefore, be able to connect every data field to a reason for collecting it, whether that is an email address, mobile number, location or account detail.
Without that connection, improving the wording of the banner merely puts better copy in front of the same underlying problem.
Most consent implementations are designed around acquisition.
Businesses optimize the point at which someone signs up, submits a form or gives consent. Withdrawal often receives less attention than acquisition.
Section 6(4) of the DPDPA is direct on this. Withdrawal must be available “at any time, with the ease of doing so being comparable to the ease with which such consent was given.”
Imagine that a customer withdraws marketing consent after their information has already reached a CRM, email platform and campaign audience. Which system receives the withdrawal first? Which applications need to stop processing? How quickly does it propagate? What prevents the same contact from reappearing when another database is synchronized?
These are routine operational questions, not edge cases. This is a workflow problem, and it sits at the heart of any DPDPA-ready privacy program
Another weakness emerges when organizations examine what they actually retain as evidence of consent.
Many systems reduce consent to a binary field: yes, or no.
That may be useful for automation, but it says very little about the original decision.
A useful consent record should allow the organization to reconstruct what happened. What interaction generated the permission? Which purpose was associated with it? What did the user do? Has the preference subsequently changed?
Section 6(10) of the DPDPA puts the burden of proof squarely on the Data Fiduciary, which must be able to demonstrate that both a valid notice and valid consent were obtained. Months later, a regulator, auditor or data principal may ask what was actually agreed to. The system needs to answer.
The DPDPA consent banner or form where a person provides information is often only the first stop.
A website form may feed a CRM. The CRM may connect with marketing technology. Customer information may appear in service platforms, analytics environments, internal reports and systems operated by processors.
The first challenge is knowing where that data actually ends up.
That means maintaining a reliable view of where relevant personal data resides and which systems use it.
That mapping capability is a core input to any serious data security and privacy program.
Consent governs permission but does not secure the data after collection.
An organization may collect personal data appropriately and still expose it through weak access controls, excessive privileges or poor monitoring.
Rule 6 of the Digital Personal Data Protection Rules, 2025 requires a Data Fiduciary to protect personal data “by taking reasonable security safeguards to prevent personal data breach.”
The listed minimum measures include encryption, access controls, monitoring logs, keeping those logs for at least one year, and requiring processors to follow equivalent safeguards.
Permission to process data and the ability to protect that data solve different problems.
Consider a financial services company preparing for DPDPA enforcement.
Its consent banner has been updated. The notice has been reviewed. Consent is being recorded.
Then the internal audit team asks a simple question: can the company show what one customer agreed to and where that decision was applied?
The answer is harder than expected.
The original consent record is no longer available in the marketing system. The CRM shows the customer receiving communication linked to a different purpose. A processor still holds data even though the customer has already withdrawn consent.
Nothing went wrong at the banner.
The failure happened after the click.
The company now has to trace how consent moves across its systems, decide which team owns each step, and make sure a withdrawal reaches every place where the data is still being used.
That is the difference between collecting consent and being able to govern it.
Consent management often involves several teams, including privacy, marketing, technology, security and business operations. The challenge is making sure each team knows exactly what it is responsible for.
For example, the privacy team may define how consent should be handled, while another team manages the system where that consent preference must be updated. If ownership is unclear, important actions can easily be missed.
A strong DPDPA program needs clear responsibility for how consent is managed across the organization.
Organizations looking to identify gaps in their current approach can explore Silverse’s DPDPA services for a focused assessment of their consent and data lifecycle.
Is having a DPDPA consent banner enough for compliance?
No. A banner captures the consent interaction at the point of collection, but the organization must also connect that decision to a specific purpose and manage what happens after the data enters its systems. The banner is only the visible layer. The compliance obligation runs across how the personal data travels, is used, and can be withdrawn later.
What should businesses check in a DPDPA consent notice?
Check whether the notice clearly identifies the personal data being requested and the purpose for which it will be processed. Vague statements such as “We value your privacy” do not meet the standard. A compliant notice gives an itemized description of the personal data along with the specified purposes, so a reader can connect each data field to a reason for collecting it.
What should a DPDPA consent record contain?
The record should provide enough context to reconstruct the decision, including the interaction that generated the permission, the associated purpose, the user action, and any later change in preference. A binary “yes” or “no” field is not enough. Months later, a regulator, auditor or data principal may ask what was agreed to, and the record needs to answer.
How should businesses handle consent withdrawal across multiple systems?
The organization should identify the systems affected by the withdrawal and ensure the changed preference reaches every relevant application, not just the collection point. In practice, this means knowing which system receives the withdrawal first, which applications must stop processing, who owns the change, and what prevents the same contact from reappearing when another database is synchronized next.
Why does data mapping matter for DPDPA consent management?
It helps the organization understand where personal data resides and which systems may be affected by a consent decision. The point of collection is often only the first stop. The same data may travel through a CRM, marketing platforms, analytics environments, and processor systems. Without a map of where it lives, the full reach of a consent choice cannot be determined.
Please fill the details below. A representative will contact you shortly after receiving your request.