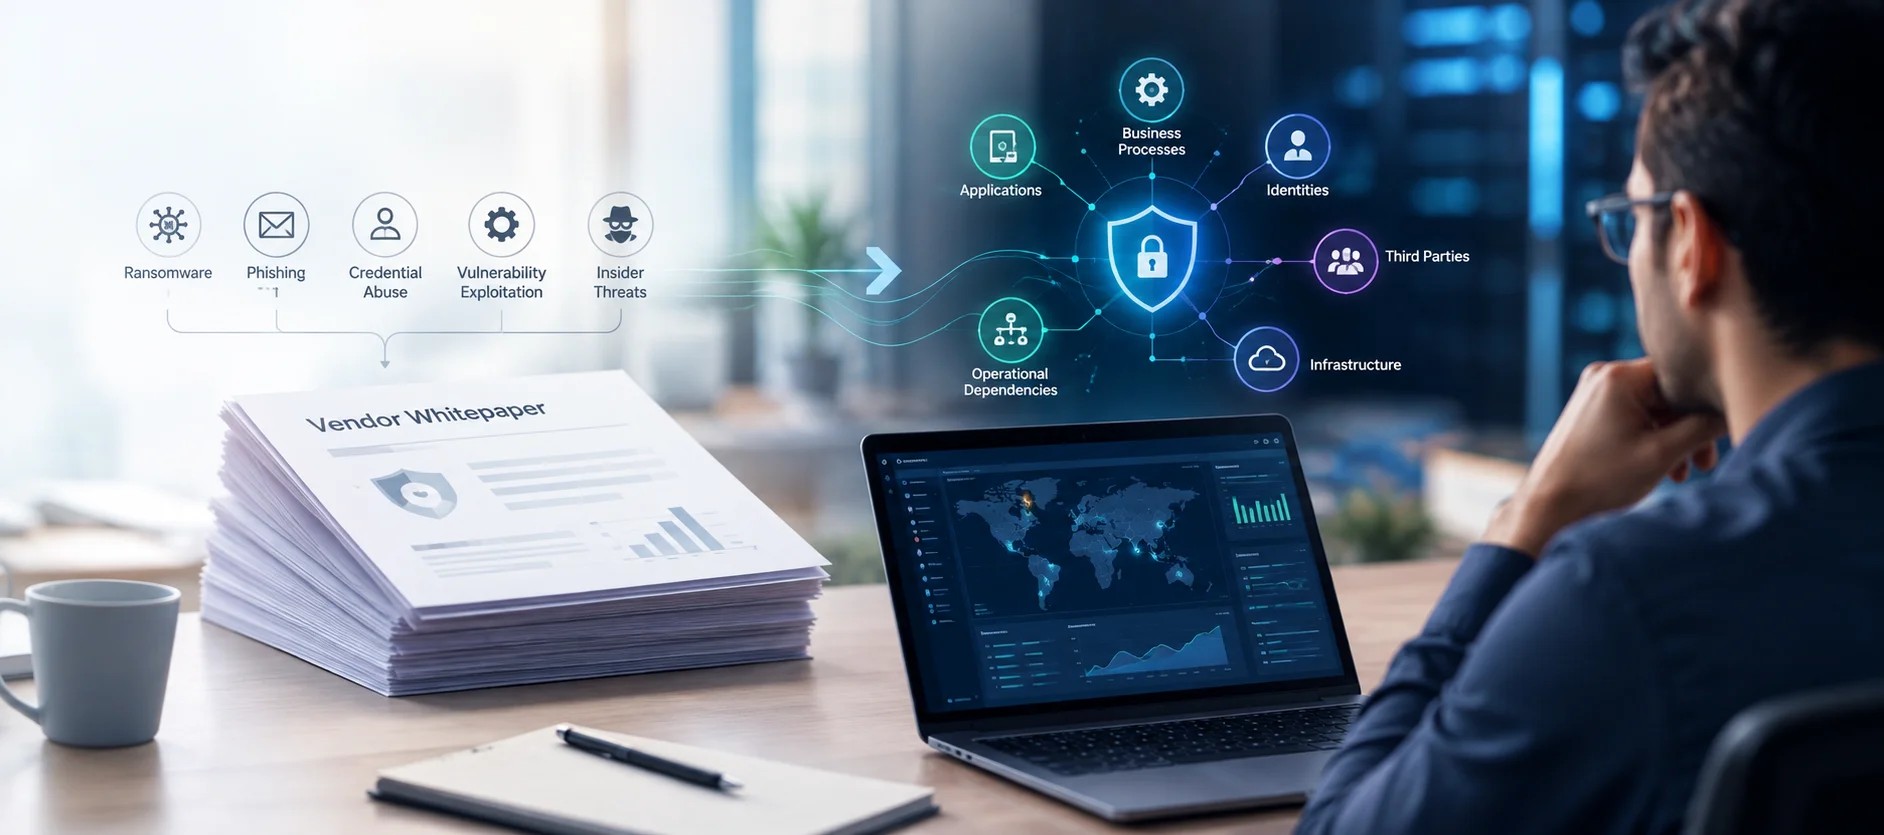
A security team can read the latest vendor whitepaper, identify the attacks affecting its industry, and still build a security program around the wrong assumptions.
The problem is not that vendor whitepapers are inaccurate, but that they are designed to show broad patterns across thousands of organizations. Your business environment is a particular combination of applications, identities, business processes, third parties, infrastructure, and operational dependencies.
That is why industry-specific cyber threats need to be understood through the way your business operates, not just through the attack categories appearing most often in reports.
This article looks at where generic threat assumptions fall short, how your critical assets and third-party connections change the attack path, and what that means for building a security monitoring program around the risks that matter to your business.
Industry-specific cyber threats tell you something about the likely targets and motivations, but they do not tell you which systems an attacker will reach first, which identities matter most, or what a successful compromise would interrupt.
Vendor reports often group incidents into familiar categories such as ransomware, phishing, credential abuse, vulnerability exploitation and insider threats. These categories are a useful starting point, but they are not a threat model. The reason is simple: two organizations in the same industry can face very different risks because their technology and the way they operate are different.
For instance, a manufacturer with connected production systems, remote maintenance access and multiple plant locations has a different attack path from a manufacturer whose most important systems are cloud applications and corporate endpoints.
Industry-specific cyber threats tell you something about the likely targets and motivations, but they do not tell you which systems an attacker will reach first, which identities matter most, or what a successful compromise would interrupt.
Vendor reports can tell security leaders what attackers are doing across a sector. The harder and more critical question is how one of those attacks would play out inside your own organization, from the first point of entry to the systems it could reach. That means starting with the business process rather than the threat name.
For instance, a healthcare organization may know that credential theft is a common threat. That information becomes much more useful once the security team works out which identities can access patient systems, which accounts can move between environments, which applications accept logins from outside the network, and where privileged access is used.
With that context, the team knows what to look for: an unusual login, a privilege change, access from an unexpected location, movement between systems or unusual activity involving sensitive applications. In short, this is the difference between knowing that a threat exists and knowing what evidence of that threat should appear in your environment.
Take the ENISA Threat Landscape 2025 report, which notes that “Phishing (60%), followed by vulnerability exploitation (21.3%) are the two leading intrusion access points.” Those percentages are useful, but they do not tell a security team which of its own applications, identities or suppliers creates the most practical exposure.
A security program built on broad threat assumptions often has plenty of alerts but limited visibility into what matters.
Understanding an organization’s exposure is only useful if its security monitoring can detect the activity associated with that exposure. A security program built on broad threat assumptions often has plenty of alerts but limited visibility into what matters.
The problem can start as early as the data entering the SIEM, because where the most useful evidence sits differs from one organization to the next:
So the issue is not simply whether a log source exists, but whether the security team has enough context to recognize suspicious activity against the systems that are at risk.
The same applies to detection rules. A rule that makes sense across a broad customer base may be of little value to one organization, while a narrower rule could be critical because it relates directly to a high-value business process.
One source of exposure that generic threat models can overlook is the access granted to third parties. Suppliers, managed service providers, cloud platforms, contractors and business partners can all create paths into systems or data. If one of those trusted connections is compromised or misused, an attacker may be able to reach internal resources through access that the organization has already granted.
The NIST Cybersecurity Framework 2.0 treats this as a governance requirement rather than an afterthought. It expects that “Suppliers are known and prioritized by criticality” and that “The risks posed by a supplier, their products and services, and other third parties are understood”.
Without that understanding, a third-party connection stays an assumed relationship of trust rather than a monitored attack path.
Understanding third-party connections is one part of a broader process: mapping the organization’s overall exposure and using it to guide security monitoring. Instead of starting from a generic list of threats, a security program built around the organization’s actual exposure works outward from the business itself, in this order:
Taken together, this turns threat detection from a broad technology exercise into an operating model built around the organization’s own risk.
Consider a financial services organization that has built its security program around the industry-specific cyber threats most frequently highlighted in industry reports. The SOC has broad endpoint coverage and several standard detections for malware, phishing and suspicious logins.
During a security review, the organization maps its most important business processes and finds a different concern. A third-party service provider has privileged access into an internal application that supports a critical financial workflow. Because the connection is legitimate, it raises little concern under the existing monitoring model, and the security team has little context linking activity from that connection to the application’s privileged functions.
Nothing in the vendor whitepapers describes this organization’s environment, but the internal mapping exercise shows that the third-party connection is a meaningful attack path. As a result, the organization can now prioritize the relevant data, examine activity around the connection and strengthen detection around the systems and identities that matter most.
The improvement came from understanding where a threat could move inside the business, not from finding another generic threat category.
No security team can predict exactly how an attacker will operate. The objective is more practical: make the security program sensitive to the paths that could cause real harm in your environment. A program built that way gives the security team a clear basis for telling background noise apart from activity worth investigating.
Silverse’s Managed Threat Detection and Response combines continuous monitoring, threat intelligence, advanced analytics and expert analysis to identify and respond to threats, while incident investigations and root cause analysis help organizations understand what happened and strengthen their response.
Talk to Silverse about assessing where your current security program may still be relying on generic assumptions.
Why are vendor whitepapers not enough to build a security program?
Vendor whitepapers provide broad information about common threats and attack techniques, but they do not describe your organization’s specific applications, identities, business processes, third-party connections or critical assets. A useful security program needs to turn those broad threats into attack paths and detection priorities that fit the organization’s own environment.
Why does critical asset mapping matter for threat detection?
Mapping the critical business processes, applications, infrastructure, identities and data first tells the security team which systems a successful compromise would interrupt and which identities can reach them. That is what allows a detection rule tied to a high-value business process to be treated as critical, instead of every alert being treated the same way.
How do third parties affect an organization’s threat model?
Third parties can create legitimate connections into applications, systems or data, which can become relevant attack paths if compromised or misused. Organizations therefore need their suppliers and other third parties to be known and prioritized by criticality, with the risks each one poses understood, so that a third-party connection becomes a monitored attack path rather than an assumed relationship of trust.
How should a SOC adapt to changing business risks?
The monitoring model should be reviewed as the environment changes. New applications, cloud workloads, vendors, business processes and privileged access paths can alter the organization’s exposure. Detection priorities should therefore be updated as the environment and its important attack paths change.
Please fill the details below. A representative will contact you shortly after receiving your request.